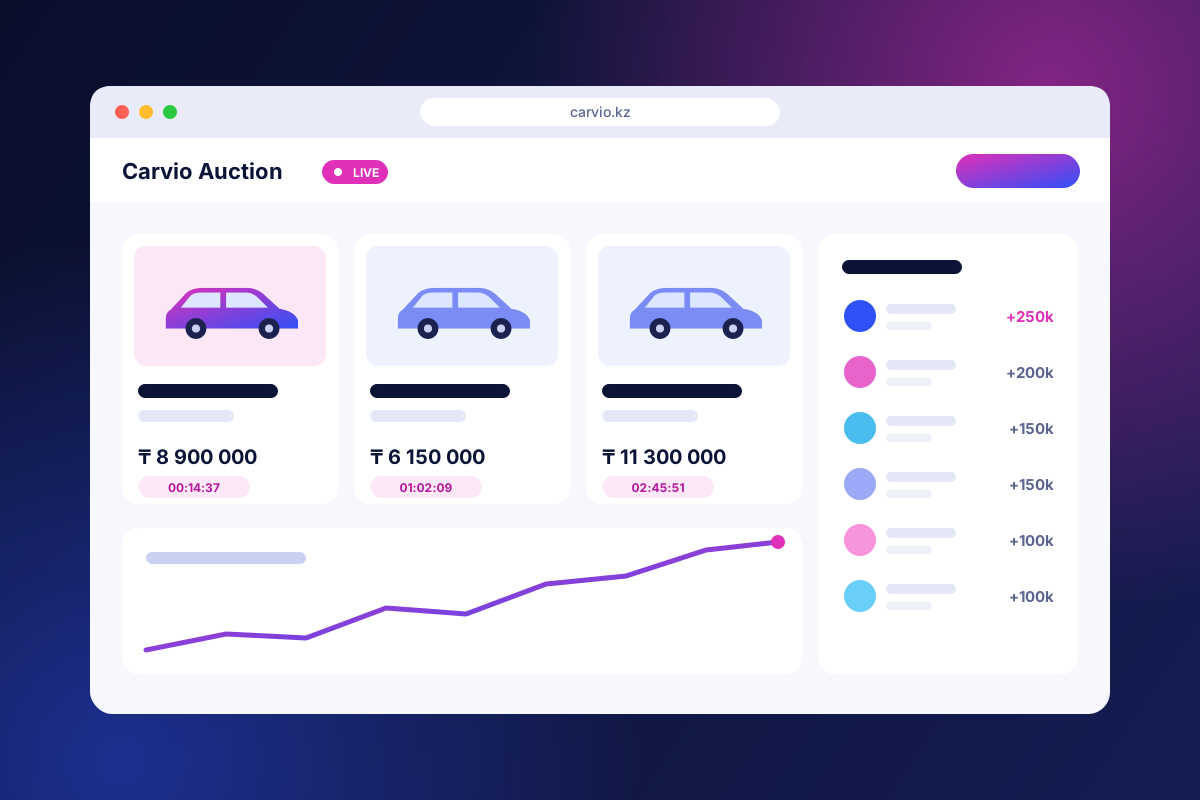
 AutoTech
Bank car auction
Carvio Auction
An auction platform for banks that sells only verified cars, inspected and valued via AvtoSan.
- Next.js
- React
- TypeScript
- Laravel
Services
We test the security of web applications, APIs and infrastructure through an attacker's eyes. You get more than a list of vulnerabilities: a prioritized action plan based on business risk — plus our support while you fix the issues.
A transparent process where you see progress at every stage.
We dive into your business, goals and processes, and define requirements and success criteria.
Architecture, UX/UI, stack selection and a roadmap with clear milestones.
Iterative development, code review, DevOps and regular demos.
QA, load testing and a security audit before release.
Deployment, monitoring and training for your team.
Support, scaling and performance optimization — we stay with you as the product grows.
AutoTechBank car auction
An auction platform for banks that sells only verified cars, inspected and valued via AvtoSan.
 LegalTech
Online legal consultations
An online legal consultation platform digitizing a historically offline industry.
Leave a request and we will get back to you with a solution, timeline and team.